For the cybersecurity industry to function properly, we depend on full disclosure, a principle much like the one described by Bruce Schneier (1) around 2007. At the time, the central argument was that publicly exposing security vulnerabilities would pressure software companies into fixing them, if only to save face under public scrutiny. Which has shaped the industry to date.
As discussed by Caruso in “Inside Cyber Warfare”, the system upon which our cybersecurity depends is morally debatable and remains the subject of heated discussion. However, the ever-expanding attack surfaces created by the ongoing wave of digitalization are exposing our societies to forms of hybrid warfare that would have been almost unthinkable just a few years ago, creating entire new landscapes.
For instance, what began as a series of attacks targeting supermarket distribution networks (2) has now expanded to potentially include essential services such as blood banks (3), which play a vital role in supporting critical infrastructure.
While the motives and identities of the perpetrators remain under investigation, it may be some time before we have any indication of who carried out these attacks—and even then, there is only a slim chance of establishing who was ultimately behind them.
From a national security perspective, supply chains falling victim to cyberattacks are equally problematic, whether the attacks originate from commercial proxy wars between suppliers or retaliation by an adversarial nation. But the results are not the same.
The reason is the fact that state-sponsored actors may be ultimately responsible for developing the malware, but this is of little consequence for assessing the deployer, when black-market actors operate under Crime-as-a-Service (CaaS) schemes. Anyone with enough means and access to a crypto wallet is a potentially responsible party.
Which leaves us with a rather complicated problem: as our digital infrastructure expands and the profitability of criminal services increases, assessing both the motivations behind cyberincidents and the risks they pose becomes increasingly difficult, while their consequences become less predictable.
After all, there is a remarkable difference between an environment of cyberespionage, operating under Spy-as-a-Service (SaaS) models, where we may be able to establish a connection between an attack and those who stand to benefit from the information obtained, and attacks intended to disrupt supply chains or other real-world operations. In the latter cases, reports and evidence may, to some extent, be deliberately fabricated to fuel regional conflicts or increase tensions between neighboring nations.
The degree of evidence and the connections that would need to be established to tie an arms dealer, for instance, to a cyberattack masquerading as a state-sponsored operation intended to incite a war is considerable. Yet such scenarios are no longer merely speculative, but represent an emerging reality that government agencies should be increasingly wary of in the coming decades.
The increased productive capacity of adversaries through AI adds yet another dimension to an already complicated scenario, one characterized by misinformation and increasingly automated operations targeting critical infrastructure. Addressing these threats will require a degree of inventiveness we have rarely seen before, particularly in our ability to discern how adversaries plan and direct their operations against us.
In an evolving threat landscape, we cannot expect conventional moral constraints to apply universally. Assuming that our adversaries would refrain from using certain capabilities simply because our own understanding of morality and law would prevent us from doing so creates a dangerous blind spot. This fits rather well with the analytical pitfalls described by Heuer in Psychology of Intelligence Analysis, particularly the tendency of intelligence analysts to interpret adversarial behavior through the assumptions and moral frameworks of their own societies
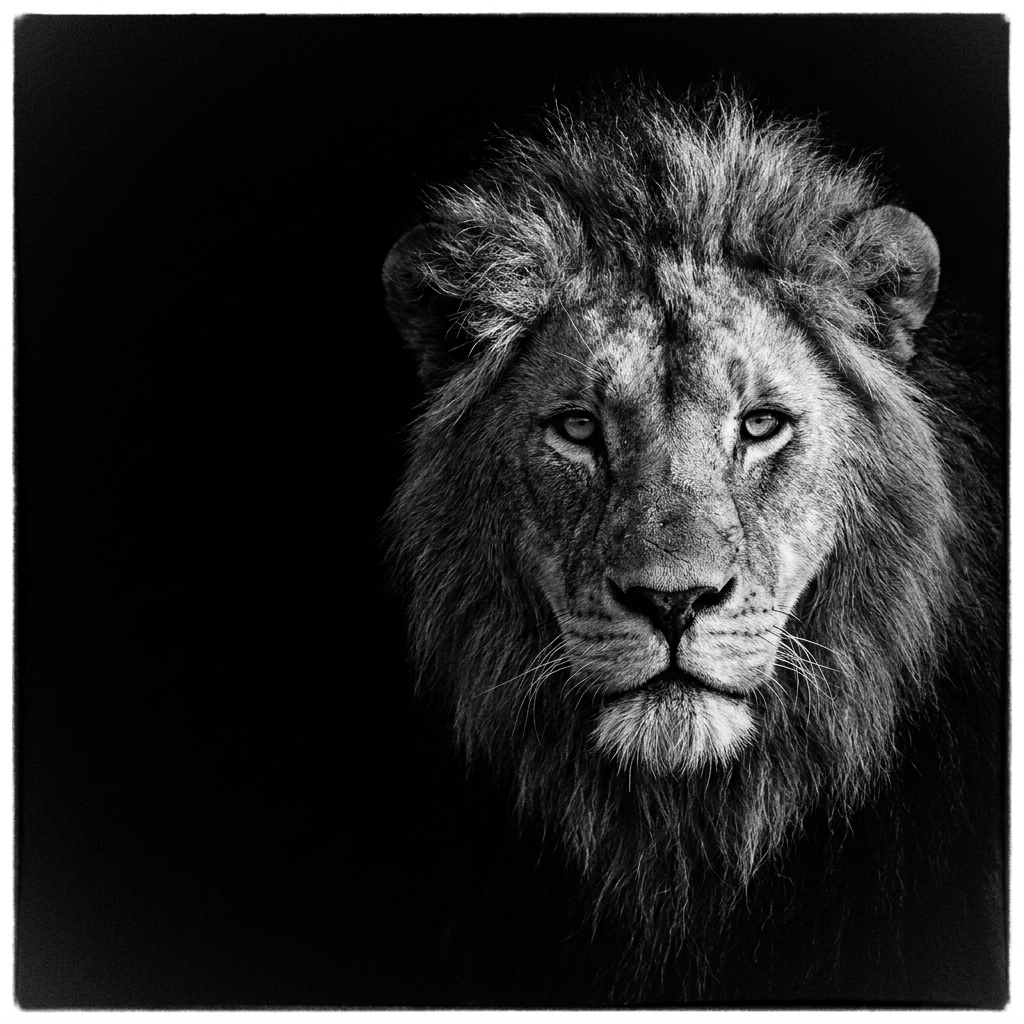
The dangers of asymmetric warfare may already be looming at our doorstep. As a society, we must be careful not to fall into the same trap as the vegetarian in the old joke, who expected the lion not to eat him out of respect for his diet.
Lions and other predators operate according to different rules, and we would be rather naive to pretend otherwise.
Notes:
- Schneier: Full Disclosure of Security Vulnerabilities a ‘Damned Good Idea’ – Schneier on Security
- Fridges in French supermarkets hit by cyber attack
- Blood banks hit by cyber attacks in France in bid to destroy supplies days after supermarket fridge hack across Europe
📕 The Pocket AI Governance Guide is out now for readers looking for a practical way to understand governance in AI.
📙 Amazon US: https://a.co/d/05z7Y2gf
📗 Europe (Amazon Germany): https://amzn.eu/d/0g8ON3Cf
(Also available through other Amazon stores.)
Explore the free articles and resources available on this website.


Share what you think!